
Key Takeaways
- ISO 27001 certification cost for a small startup typically runs 6,000 to 25,000 dollars in year one, with mid sized companies often landing between 25,000 and 70,000 dollars depending heavily on team size and implementation path.
- The certification audit fee itself is usually the smallest line item, implementation, whether DIY, consultant led, or platform assisted, is typically the largest cost variable.
- ISO 27001 is not a one time cost, annual surveillance audits and a three year recertification cycle continue after year one.
- Compared to SOC 2, ISO 27001 tends to cost more and take longer for a first time certification, though the two are not always an either or choice for a growing startup.
ISO 27001 certification cost varies more widely across published estimates than almost any other compliance framework, largely because the total depends on three genuinely different cost drivers, company size, implementation approach, and how mature your existing security program already is before you start. For a startup budgeting this for the first time, understanding which of those three is actually driving your number matters more than any single published figure.
Cost by Company Size
Published estimates for 2026 converge into a rough pattern once you sort by company size, though real numbers vary by region and certification body.
| Company size | Typical first year cost |
|---|---|
| Micro, 1 to 10 employees | 6,000 to 15,000 dollars |
| Small, 10 to 25 employees | 15,000 to 30,000 dollars |
| Growing SaaS startup, 25 to 100 employees | 30,000 to 70,000 dollars |
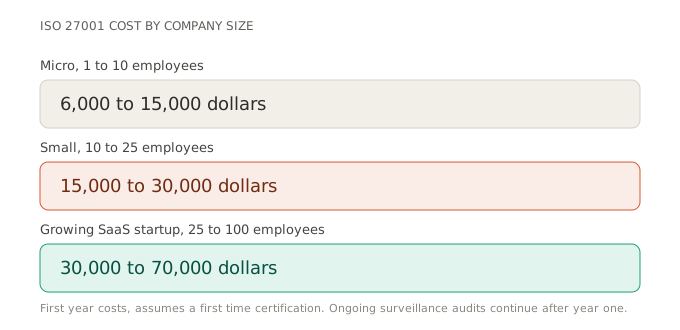
These ranges assume a first time certification. Even the low end assumes you are starting mostly from scratch, building an information security management system, drafting policies, and closing gaps before the actual audit can happen.
What Actually Drives the Cost
The certification audit fee, paid to an accredited certification body for the mandatory Stage 1 and Stage 2 audits, is usually not the biggest number on your invoice. ISO 27001 audit fees for a small organization typically run a few thousand to around eight thousand dollars, driven mostly by required audit days based on your headcount. The bigger cost variable is implementation, closing the gap between where your security program is today and what ISO 27001 actually requires. A do it yourself approach using templates and internal effort can keep ISO 27001 cost for startups low but takes real internal time. A consultant led implementation costs more upfront, often 15,000 to 30,000 dollars or more, but moves faster and reduces the risk of failing the audit on a first attempt.
Not sure whether ISO 27001, SOC 2, or both make sense for your current stage and buyer base? Book a scoping call and we will help you figure out which framework your actual pipeline needs.
ISO 27001 Certification Cost vs SOC 2
This is where framework choice becomes a real budgeting decision, not just a compliance one. ISO 27001 vs SOC 2 cost is not a close comparison for a first time small startup, ISO 27001 generally runs higher, and the certification cycle itself, Stage 1 and Stage 2 audits followed by annual surveillance audits and a three year recertification, is a longer term commitment than SOC 2’s annual audit cycle. Our ISO 27001 vs SOC 2 pentest comparison covers how the two frameworks differ specifically on penetration testing expectations, which is a smaller piece of the overall cost but still worth scoping correctly for either path, and a well scoped SaaS penetration test can typically support both frameworks at once if timed correctly.
For companies selling primarily into the US, SOC 2 is usually the faster, less expensive starting point. ISO 27001 becomes the more relevant framework once a company has meaningful UK, EU, or international enterprise customers who expect it specifically.
Why This Is Not a One Time Cost
ISO 27001 certification does not end at the audit. Annual surveillance audits, typically 4,000 to 7,000 dollars each, are required to maintain certification, followed by a full recertification audit at the three year mark that roughly matches the original certification cost. Budgeting for ISO 27001 certification cost as a single upfront number, without accounting for this ongoing cycle, is one of the more common planning mistakes startups make when they first commit to the framework.
Frequently Asked Questions
What is the cheapest way to get ISO 27001 certified? A do it yourself implementation using templates and internal effort, paired with the minimum required audit days, is the lowest cost path, typically landing in the 6,000 to 15,000 dollar range for a very small company. This trades cost for internal time and higher execution risk.
Does ISO 27001 cost more than SOC 2? Generally yes, for a first time certification. ISO 27001’s audit structure and ongoing surveillance cycle tend to make it a larger, longer commitment than a typical SOC 2 Type 2 engagement, though the gap narrows for companies that already have mature security documentation in place.
Is ISO 27001 certification a one time expense? No. Certification requires annual surveillance audits to remain valid, and a full recertification audit at the three year mark, both of which should be budgeted as ongoing costs rather than a single upfront number.
If you are trying to figure out whether ISO 27001 certification cost fits your current budget and buyer base, book a scoping call and we will walk through what your specific situation actually requires.
Packet33 is a penetration testing and compliance advisory firm serving SaaS and HealthTech startups in the US, Canada, and UK.

Mohamed is the founder of Packet33. He worked as a cybersecurity analyst before launching the firm and now leads an OSCP-certified team serving SaaS and HealthTech startups in the US, Canada, and UK.