
Vendor details below are based on each company’s public website as of the publish date. Company information changes, so confirm current scope, pricing, and capabilities directly with each vendor before relying on them.
Key Takeaways
- There is no single best option among HIPAA pentest vendors. The right fit depends on your stage, your product, and whether you need a pentest alone or a broader HIPAA program.
- HIPAA does not name penetration testing as a standalone requirement today, but it does require ongoing risk analysis, and most buyers use a pentest as evidence of that work.
- This list is unranked and Packet33 is included because we wrote it, not because we claim to be the best fit for every company.
- Ask every vendor how they handle PHI during testing, whether they will sign a business associate agreement, and whether the report maps to what your auditor or health system buyer expects.
Searching for HIPAA pentest vendors usually means a health system buyer, a security questionnaire, or an upcoming risk assessment has put penetration testing on your plate for the first time. This list covers five providers with different models, so you can match a vendor to your situation instead of comparing quotes that are not really comparable.
What to Know Before Comparing HIPAA Pentest Vendors
The HIPAA Security Rule requires covered entities and business associates to conduct an accurate and thorough risk analysis and to evaluate their safeguards periodically. HHS summarizes those requirements, and a penetration test is one of the most common ways HealthTech companies produce evidence for them. The proposed Security Rule update published in January 2025 would make annual penetration testing an explicit requirement, though it has not been finalized.
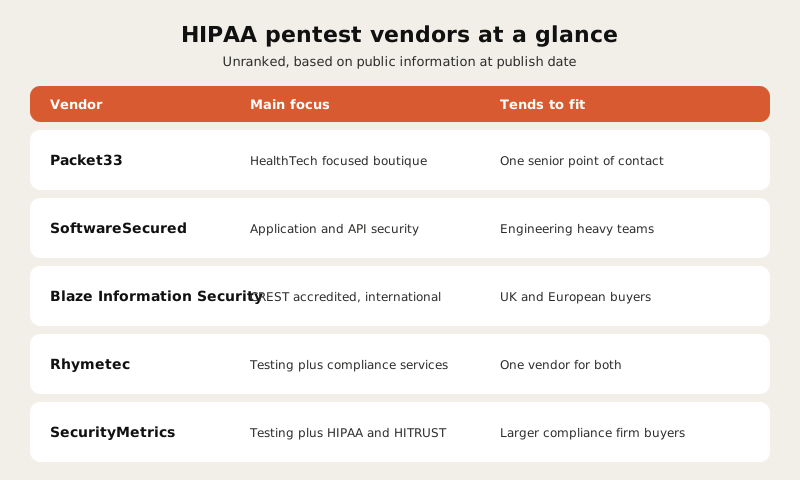
Because the rule leaves the method open, vendors vary a lot in what they deliver. Some focus on application testing, some bundle testing with compliance services, and some center on HIPAA risk analysis with testing as one option among several.
Packet33
Packet33 is a boutique penetration testing and compliance advisory firm serving SaaS and HealthTech startups in the US, Canada, and UK. Our delivery team holds OSCP, CRTP, and CARTP certifications, and every engagement is scoped and managed by a single point of contact from first call through delivery. Our HIPAA work is built around HealthTech products specifically, including the APIs and integrations that move PHI between systems.
Best for: HealthTech startups from pre seed through Series A and beyond that want a senior team built around their industry, with one point of contact who stays with them across repeat engagements.
SoftwareSecured
SoftwareSecured is a Canadian application security firm. Its HIPAA penetration testing page says it serves healthcare providers, payers, and HealthTech companies, with a focus on EHRs, APIs, and healthcare platforms, and it states that it has delivered over 2,000 pentests in the last five years. The page also describes audit ready reporting, remediation guidance, and retesting within twelve months of the report.
Best for: engineering heavy HealthTech teams that want a vendor whose practice is built around application and API security.
Blaze Information Security
Blaze Information Security is a CREST accredited provider founded in 2016 and headquartered in Porto, Portugal. Its site lists Healthcare and Life Sciences among the industries it serves and includes a dedicated HIPAA solutions page, alongside displayed CREST, ISO 27001, and SOC 2 badges.
Best for: HealthTech startups with a UK or European customer base, where CREST accreditation often carries weight in procurement conversations.
Rhymetec
Founded in 2015 and based in New York, Rhymetec combines penetration testing with compliance services, and its site states that more than 1,200 companies work with it. HIPAA appears on its list of supported frameworks, and it has a dedicated HealthTech industry page. Its testing coverage includes web, mobile, API, network, and cloud assessments.
Best for: HealthTech startups that want one vendor covering pentesting alongside broader compliance work such as vCISO support and readiness, instead of coordinating several providers.
SecurityMetrics
SecurityMetrics offers external, internal, application, mobile, network, and segmentation penetration testing alongside a wide set of compliance services. Its site includes HIPAA compliance and audit offerings, a healthcare industry page, and states that its testers have experience with standards such as PCI, HIPAA, and HITRUST and hold certifications including CISSP, OSCP, and BSCP. It also lists HITRUST Authorized CSF Assessor status.
Best for: HealthTech companies that want penetration testing from a larger compliance firm that also covers HIPAA and HITRUST work, instead of a smaller specialist.
Narrowing down which model fits your product and your next health system review? Book a scoping call and we will talk through it directly, with no obligation either way.
How to Choose Among HIPAA Pentest Vendors
Fit matters more than brand. A few practical questions separate the options:
- How is PHI handled during testing? Ask whether testing runs against synthetic data, and whether the vendor will sign a business associate agreement if testers could encounter PHI.
- Does the report map to HIPAA language? SOC 2 style reports and HIPAA risk analysis evidence are not always the same thing, so ask how findings tie to the risk analysis and evaluation requirements.
- Who actually tests? Ask who will do the work, what certifications they hold, and whether the same people return next year.
- Does the scope cover your real PHI paths? APIs, integrations, and mobile apps should be in scope if they touch patient data.
For a breakdown of what drives price across these models, see our HealthTech penetration testing cost post.
FAQ
Does HIPAA require penetration testing? Not by name today. HIPAA requires ongoing risk analysis and security evaluation, and many organizations use penetration testing to support that. A proposed update from January 2025 would make annual testing mandatory, but it is not final.
Do I need a vendor that specializes in HIPAA? Not necessarily, but you want one that understands PHI flows and can structure the report for HIPAA and health system reviewers. Ask for specifics instead of relying on a logo.
Can one vendor cover both SOC 2 and HIPAA? Often, if the scope and timing align, but the frameworks weight evidence differently, so confirm the report format with your auditor and your HIPAA lead.
How often should a HealthTech startup get a pentest? At least annually, and after significant changes such as a new integration, a major release, or a change to how PHI is stored or shared.
If you want a HIPAA aware pentest scoped to your actual product, book a scoping call, or start with our HIPAA penetration testing page for the full breakdown of what is included.
Packet33 is a penetration testing and compliance advisory firm serving SaaS and HealthTech startups in the US, Canada, and UK.

Mohamed is the founder of Packet33. He worked as a cybersecurity analyst before launching the firm and now leads an OSCP-certified team serving SaaS and HealthTech startups in the US, Canada, and UK.